EDGE End User Devices
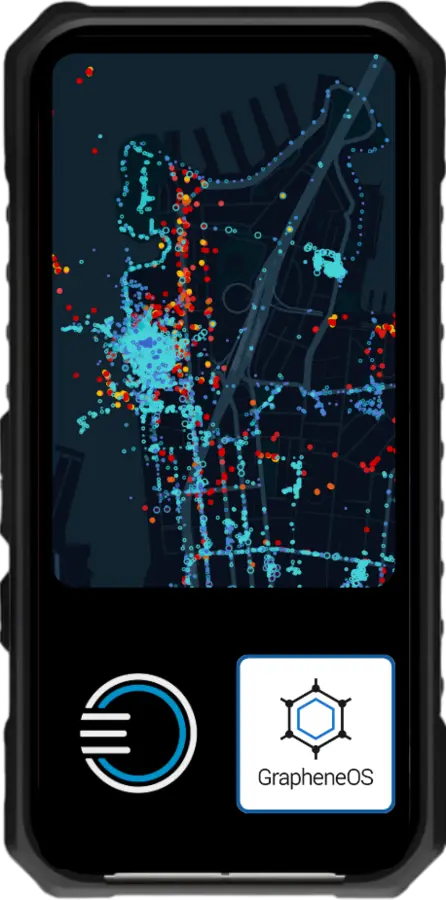
Hardened GrapheneOS endpoints configured for secure operational use.
Verified bootEncrypted dataDuress wipeManaged deployment
Each component is selected for its role, then prepared and supported as part of the complete system.
Hardened GrapheneOS endpoints configured for secure operational use.
Dedicated ATAK infrastructure deployed and supported around the requirement.
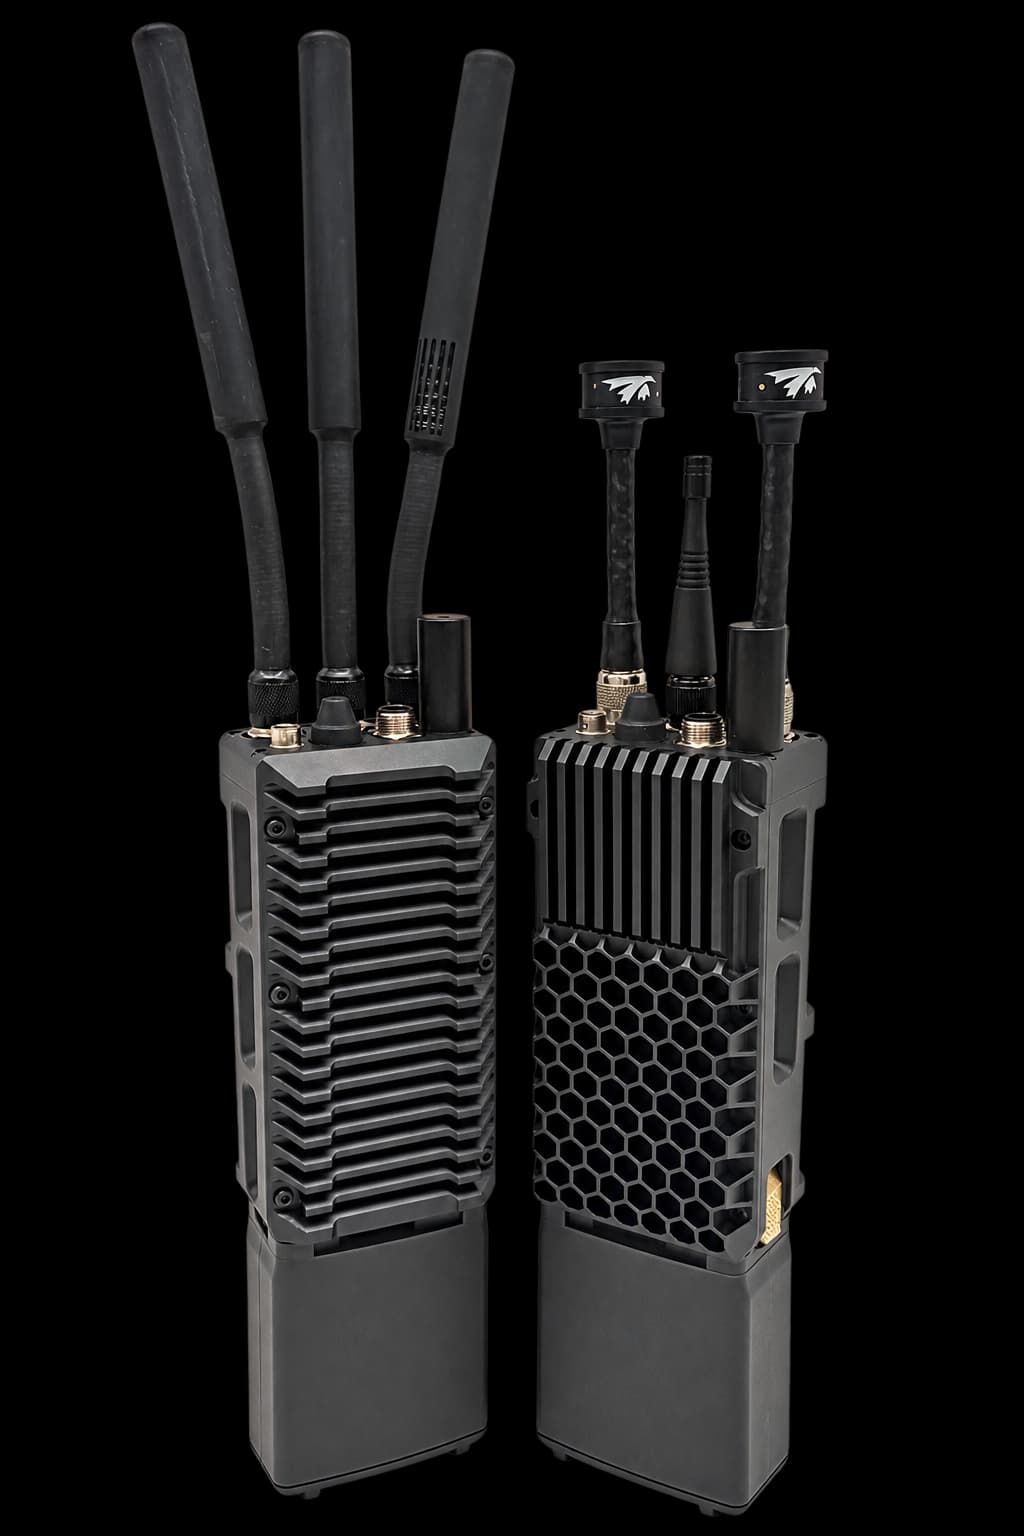
Resilient connectivity configured across field, vehicle and fixed locations.
Anonymous eSIMs, VPNs and encrypted apps configured as a private operational communications layer that does not require identification.
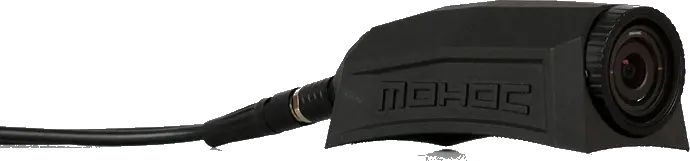
Live video, drones, trackers and specialist sensors connected to the common picture.
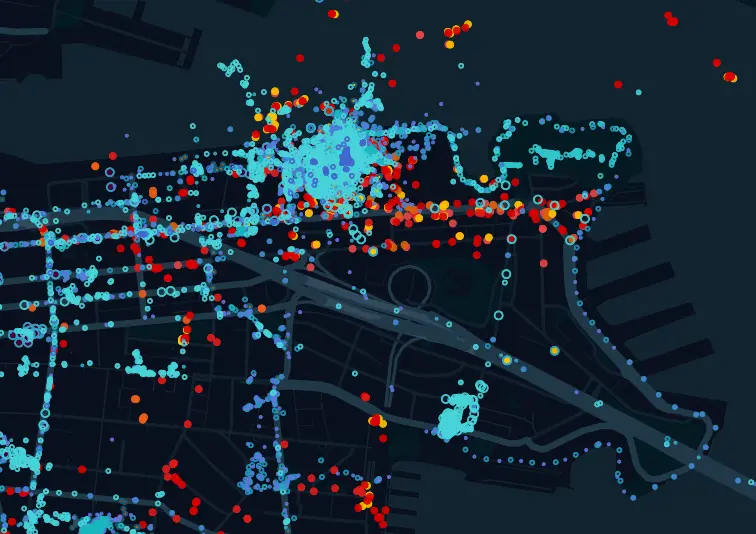
Digital intelligence. Force protection. Operational awareness.
Request Overwatch Support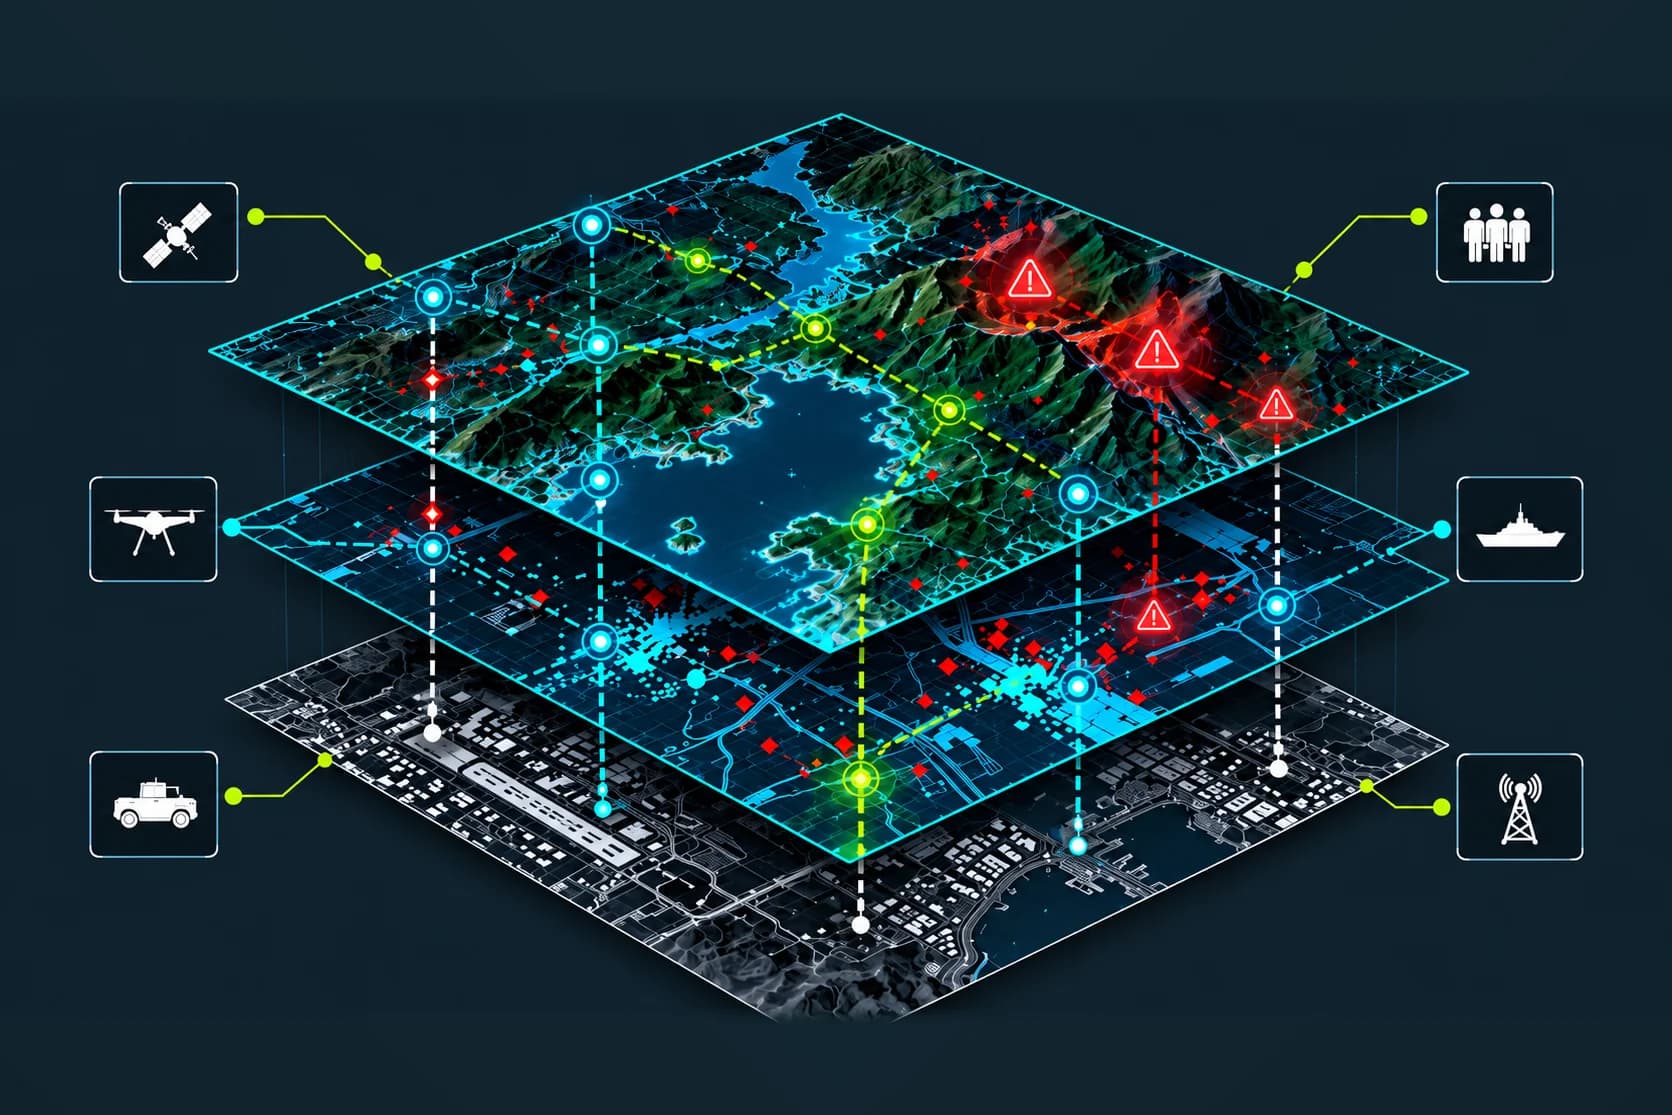
Specialist plugins, APIs and customer systems integrated as one controlled layer.
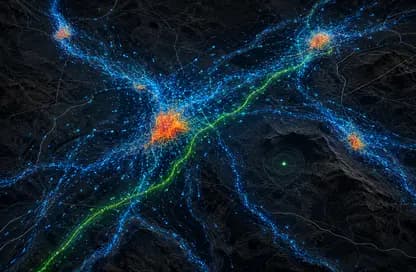
Operational movement intelligence supporting crowd awareness, migration response and missing person search and rescue missions.
A GrapheneOS EDGE EUD provides strong application sandboxing, exploit mitigations, verified boot, rapid security updates and encrypted data protection. Configurable automatic reboot returns the device to a locked state, while a duress PIN or password can trigger an immediate wipe.
Where remote wipe is required, it can be implemented through an approved mobile device management solution, with the command channel and associated trust risks assessed separately.
The operating environment determines the device, network, server, sensor and support model. Custom equipment and integrated solutions may have varied lead times and warranty conditions depending on configuration and application.
Define Your Requirement